
www.electronics-usa.com
13
'26
Written on Modified on
Tamper-Resistant Adaptive SoC Protects Against Backside Physical Attacks
AMD Versal TR devices bond a sensor die to the compute die, securing cryptographic keys in defence and fintech systems.
www.amd.com
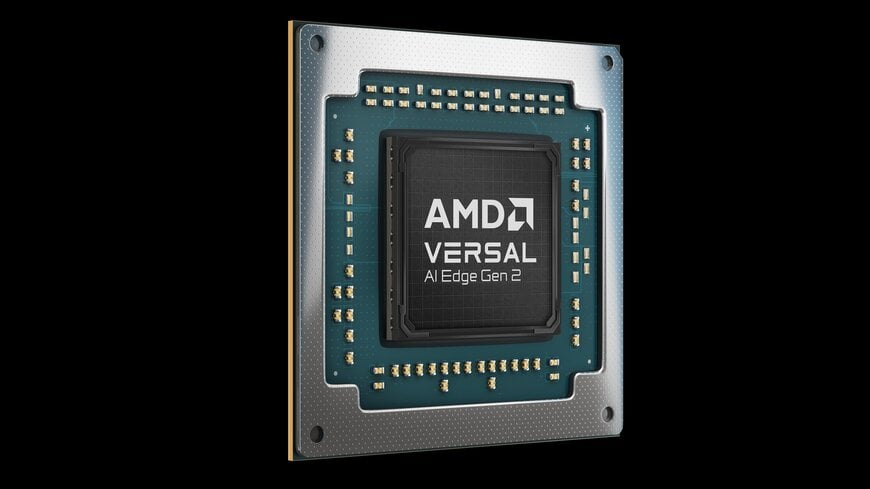
Security-critical embedded systems in defence, data center networking, fintech and industrial infrastructure increasingly face attackers who have physical access to the hardware. AMD has addressed this threat with Versal tamper-resistant (TR) devices, adaptive SoCs that integrate protection against silicon backside attacks with high-performance heterogeneous compute.
Why Physical Attack Protection Matters in Embedded Hardware Security
Physical attacks target the silicon itself rather than software interfaces. Techniques such as optical probing, laser fault injection or voltage glitching can extract cryptographic keys or alter device behaviour once an attacker has access to the chip. Until now, system designers seeking higher protection levels have typically built custom solutions from mechanical enclosures, ASICs and additional components. These approaches add development cost, require specialist resources and increase verification effort and re-spin risk. According to AMD, Versal TR devices are the industry's first adaptive SoC or FPGA-based devices with built-in protection against physical attacks on the silicon backside.
How the 3D-Bonded Protection Die Works
The core of the tamper-resistant FPGA architecture is a sensor-based protection die bonded to the main compute die using 3D active-on-active technology. This die shields the entire backside of the device, protects sensitive information and detects physical attacks. If the protection die is tampered with or removed, the device is prevented from booting. Because protection is integrated at package level, a single device can replace separate compute, security and enclosure-based components. This saves board area and simplifies board design compared with custom solutions.
AMD states that tamper-resistant does not mean tamper-proof: protection applies to specified physical attack methods, and the applicable threat model and limitations are described in the product documentation.
Post-Quantum Cryptography and Layered Key Protection
In addition to backside protection, the devices combine several physical and cryptographic safeguards:
Expanded hardware acceleration for post-quantum cryptography, with new support for the Module-Lattice-Based Digital Signature Algorithm (ML-DSA) and the Stateless Hash-Based Digital Signature Algorithm (SLH-DSA).
Hybrid boot flow support, allowing multiple signature algorithms to be used during secure boot.
Application security unit (ASU) key vault improvements and a new memory element aging sensor (MEAS), providing additional safeguards for cryptographic keys.
Expanded glitch detection, combining an improved Versal glitch detector with a new orthogonal glitch detector that also covers glitches occurring simultaneously across two voltage rails.
Technical Specifications of the Versal TR Portfolio
Versal TR devices are based on Versal AI Edge Series Gen 2 adaptive SoCs. They integrate Arm CPUs, AI Engines, programmable logic, hard IP and connectivity, delivering up to 229,000 DMIPS of scalar compute, up to 369 INT8 TOPS and up to 543,000 LUTs. The portfolio comprises three devices, 2VE3358TR, 2VE3558TR and 2VE3858TR, providing a common platform for different performance and cost requirements.
Design Migration and Industrial Applications
Each Versal TR device has a footprint-compatible standard counterpart that is already available. Engineers can develop on the standard Versal AI Edge Series Gen 2 device and transition to the tamper-resistant version without rerunning synthesis or place and route, keeping the design intact. This reduces the time-to-market penalty usually associated with custom security hardware. Typical applications include defence systems, data center networking equipment, fintech platforms and critical industrial infrastructure where sensitive data must remain protected even if hardware falls into the wrong hands.
Kirk Saban, Corporate Vice President, Product, Software and Solutions, AMD Embedded, said: "Protecting critical information requires continued innovation in silicon security capabilities to stay ahead of emerging threats."
Availability
The first Versal TR devices are expected to sample in the second half of 2027, with production planned for the first half of 2028.
Additional Context:
This section details technical specifications and competitive benchmarking not included in the original product announcement.
Device-level anti-tamper features already exist in secure FPGAs, but they have mainly targeted side-channel and environmental attacks. Microchip's PolarFire and PolarFire SoC families, for example, use non-volatile flash configuration, licensed differential power analysis (DPA) countermeasures, on-chip voltage, temperature and clock monitors, and a tamper response interface that can zeroize keys and design data. Protection against backside attacks, which typically involve thinning the substrate for optical probing or laser fault injection, has generally been implemented at board or enclosure level using active meshes and potting. The AMD approach moves this shielding into the device package as an active sensor die. On the cryptographic side, ML-DSA and SLH-DSA were standardised by NIST in August 2024 as FIPS 204 and FIPS 205. ML-DSA is also among the algorithms specified in the NSA CNSA 2.0 suite, making hardware support relevant for defence designs with long service lives.
Edited by Natania Lyngdoh, Induportals editor, with AI assistance.
www.amd.com
